The gold standard for connecting your OWN devices, and a poor substitute for a consumer VPN - which is exactly what it says on the tin. Tailscale is a WireGuard mesh coordinator: traffic flows device-to-device end-to-end encrypted, the closed-source coordination server sees device/key/connection metadata including which nodes talk to which, and exit nodes are your own machines unless you pay for the Mullvad add-on. The free Personal tier (6 users, unlimited devices, verified live 2026-11-02) is genuinely generous and homelab communities adore it. Honest caveats: no public audit of the closed control plane (SOC 2 and Latacora reports are on-request only), client logs stream to Tailscale by default unless disabled, business payments are non-refundable per the terms, and October 2026's uncoordinated 'Tailworm' disclosure (11 SSH findings, root socket-forwarding escalation, fixed in v1.104.4) showed how fast a trusted tool can need urgent patching. Fully self-hosted users escape the trust question via Headscale, the third-party open-source control server - which Tailscale tolerates rather than builds. Dossier data quality: all operator pages, GitHub files, Wikipedia, the independent review, news, the Tailworm report and community archives were fetched live by this site on 2026-11-02; the coordination backend itself cannot be independently verified by anyone outside the company.
auditopen source3 red flagsfacts verified - operator pages (pricing, security, privacy policy, how-tailscale-works, exit-nodes docs, security bulletins, SSH investigation page, SSH findings blog, Series C blog), GitHub README + BSD-3 LICENSE + issue 498, Wikipedia, The Proof Desk review, Network World, Tailworm report, HN Algolia and Reddit arctic-shift archives all fetched live 2026-11-02; BleepingComputer and The Hacker News returned 403 (Cloudflare) and are cited from search-result snapshots only
October 2026 'Tailworm' incident: Cyberdione Labs published 11 findings in tailscaled v1.104.2 and headscale v0.29.5 with uncoordinated disclosure; root-privileged SSH Unix-socket forwarding could reach the Docker socket and tailscaled local API; fixed in v1.104.4 within days (fast response, but SecurityWeek and BleepingComputer noted a stolen device key stays valid until deleted at the control plane - reimaging the machine does not revoke it)
Five Eyes jurisdiction (Canada) plus a closed-source control plane: this is the whole argument for Headscale, NetBird or plain WireGuard if your threat model includes the operator itself
Heavy VC trajectory: $275M total funding and a $1.5B valuation (Bloomberg, 2025-04-08), first acquisition Border0 (2026-03-17, BetaKit/Bloomberg) and an enterprise pivot toward PAM and AI governance - the homelab product is now the top of a commercial funnel, though the free tier has so far been preserved and even widened (3 to 6 users in 2026)
Review
draft generated by Qwen3, fact-checked by the vpncomparison editorial desk · review version 3 · prose updated 2026-11-02 · facts as of 2026-11-02 · how we verify
Honesty note: we have not run our own tests on Tailscale (managed WireGuard mesh) yet (leak tests, speed, kill switch). Everything on this page is source-based meta-research with dated links. When we test it, results appear here and on the change log.
Overview
Tailscale (managed WireGuard mesh) homepage - live capture 2026-09-29
Tailscale is a hosted WireGuard mesh coordination service that simplifies private network setup between your own devices. It’s not a consumer VPN - traffic stays end-to-end encrypted, but the closed-source control plane collects connection metadata. Operated by Tailscale Inc. in Canada (a Five Eyes country), it's ideal for self-hosters and remote access, but you must trust the operator with device and peer relationship data.
Logging & privacy
Tailscale claims it cannot see your traffic due to WireGuard’s end-to-end encryption, and DERP relay code is open source to verify they forward only ciphertext. However, the coordination server - closed source - collects metadata: device names, public keys, IP addresses, OS types, timestamps, and Inter-Node Traffic Logs showing which devices communicate and approximate data volumes. This is a "policy-only" logging claim with no public audit of the control plane. While SOC 2 Type II and Latacora audits exist, they’re available only on request. Jurisdiction in Canada raises concerns for high-risk users, and there’s no warrant canary.
Pricing & the renewal trap
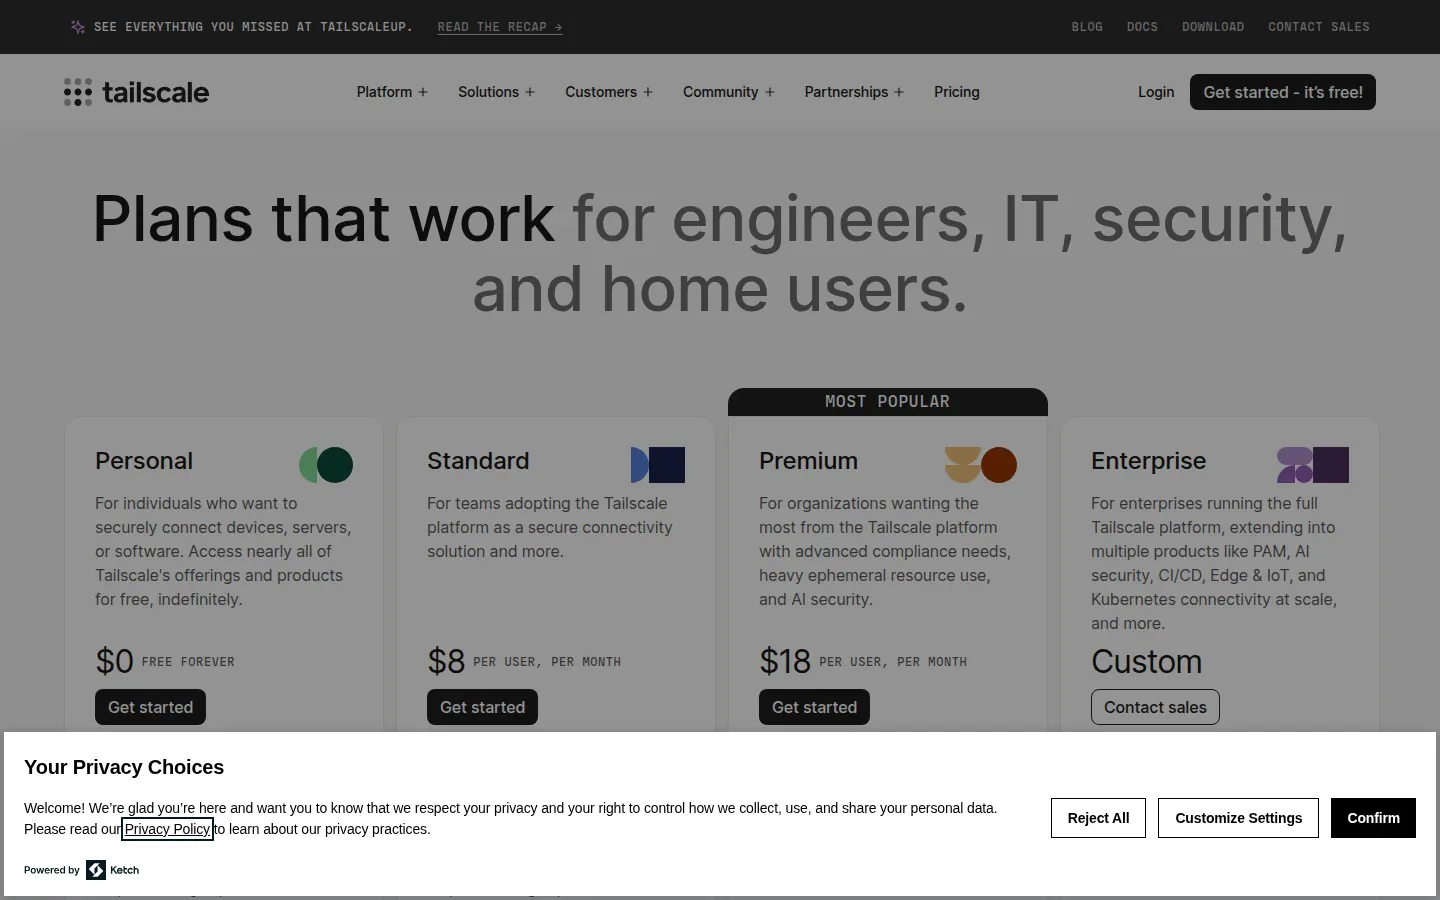
Tailscale (managed WireGuard mesh) pricing page - live capture 2026-09-29
Tailscale’s Standard business plan costs $8 per user per month, with no change at renewal - the derived renewal ratio is 1. There’s no refund window (0 days), and payments are non-refundable per the Terms of Service. The free Personal plan supports up to 6 users and unlimited devices, verified live in 2026. No multi-year pricing or intro discounts exist, so the renewal trap is neutralized by flat pricing. Payment is fiat-only; crypto is not accepted.
Built on WireGuard, Tailscale offers split tunneling, peer-to-peer routing, and optional exit nodes (your own devices or Mullvad add-on). It supports Windows, Mac, Linux, Android, iOS, and routers. No multihop, dedicated IPs, Tor over VPN, or obfuscation. Servers and countries count are irrelevant - this is a mesh, not a traditional VPN network. P2P is enabled by default; streaming geo-unblocking isn’t supported. No kill switch is documented. We haven’t run performance tests, but WireGuard ensures low latency when direct P2P works; DERP relays handle NAT traversal with minimal overhead.
Ownership & track record
Ownership details are not publicly disclosed. Tailscale Inc., based in Toronto, has raised $275M in funding and acquired Border0 in 2026, signaling an enterprise pivot. The 2026 "Tailworm" incident revealed 11 vulnerabilities, including root-level SSH escalation, though exploitation required prior access to an authorized device. Fixes shipped quickly, but the uncoordinated disclosure and lack of public audit for the control plane remain concerns. Data quality is verified across operator pages, GitHub, Wikipedia, and community archives, but the core coordination server remains unverifiable by independent parties.
Censorship resistance
Tailscale does not offer obfuscation and is not designed for use in heavily censored environments like China or Iran. Its reliance on direct UDP for WireGuard and DERP relays makes it easily detectable and blockable. Without traffic masking, this tool should not be used where circumvention of state-level censorship is required. Alternatives like Shadowsocks or obfuscated WireGuard setups are more suitable.
Verdict
Tailscale is the best choice for securely connecting your own devices with minimal setup - perfect for homelabs, NAS access, or remote work. It’s not a privacy tool for anonymity or streaming. You pay for convenience, not secrecy, and must trust Tailscale with metadata. The free tier is generous, pricing is flat, and the ecosystem is well-supported. No evidence suggests Tailscale pays review sites to promote it.
++ What holds up
Free Personal plan: up to 6 users and unlimited devices, no card required (live pricing page 2026-11-02)
End-to-end WireGuard encryption; private keys never leave devices; DERP relays only forward ciphertext (operator security page fetched 2026-11-02)
Open-source BSD-3 clients and DERP relay code, and a thriving third-party self-host path via Headscale
Frictionless: SSO login, NAT punching that just works, and the tailnet keeps working even when the coordination server is down (operator docs)
Mullvad exit-node add-on at $5/month per 5 devices borrows a genuinely respected no-logs operator
Security transparency: public CVE-style security bulletins, and the Oct 2026 Tailworm response went from disclosure to patched release in about 4 days
-- What to watch
Closed-source coordination server sees your device inventory, public IPs and which nodes connect to which - trust in Tailscale Inc. is structural
No public audit report: SOC 2 Type II and ongoing Latacora audits are on-request or account-gated only
Not an anonymity VPN: no rented server network, exit nodes are your own machines, streaming and geo-unblocking are out of scope
Payments are non-cancelable and non-refundable per the Terms of Service (fetched 2026-11-02)
Client session logs go to log.tailscale.com by default unless you opt out with --no-logs-no-support
Feature sprawl since 2024 (PAM, Aperture AI gateway, DNS filtering) - community voices warn the simple core is getting buried under enterprise add-ons
Pricing reality check
Intro price
$8 /user/mo · renews $8/mo
Renewal price
$8/mo
Notes
Personal plan is $0 forever (live pricing page 2026-11-02). Business: Standard $8 per user/month, Premium $18 per user/month, Enterprise custom. Add-ons: Mullvad exit nodes $5/month per 5 devices, extra tagged resources $1/month each. Terms of Service (fetched 2026-11-02): payments 'non-cancelable, non-transferable, non-refundable'.
email or SSO identity required (Google, Microsoft, GitHub, Okta, etc.); no government-ID verification
Payment
fiat
Apps
windows, mac, linux, android, ios, router
Check the renewal price above before any multi-year plan - true-cost calculator.
Is Tailscale legit?
Legal domicile: Canada - Tailscale Inc., Toronto, Ontario (Wikipedia, Bloomberg); a Five Eyes member country; privacy policy names processing locations in Canada, Germany, the US and the UK. Logging claim: Tailscale cannot read your traffic: end-to-end WireGuard encryption, private keys never leave devices, DERP relays only forward ciphertext; the coordination server collects device and connection metadata only - evidence class: promise only (no proof). No incidents on file in our research - absence of evidence is not proof of innocence. Facts verified - operator pages (pricing, security, privacy policy, how-tailscale-works, exit-nodes docs, security bulletins, SSH investigation page, SSH findings blog, Series C blog), GitHub README + BSD-3 LICENSE + issue 498, Wikipedia, The Proof Desk review, Network World, Tailworm report, HN Algolia and Reddit arctic-shift archives all fetched live 2026-11-02; BleepingComputer and The Hacker News returned 403 (Cloudflare) and are cited from search-result snapshots only (not fully verified) as of 2026-11-02 - read the sources below.
The money trail - what review sites earn by recommending this
affiliate status not verified yet
If we sign up for this program, every link here becomes rel="nofollow sponsored" and routes through /go/. Until then our links point straight to the provider's website with zero tracking. Ranking logic physically cannot read affiliate fields - here is the proof.
On the website
Captured by our screenshot bot from the live site (or its public archive). A capture is evidence of what the page showed at capture time - not an endorsement.
Tailscale (managed WireGuard mesh) homepage - live capture 2026-09-29Tailscale (managed WireGuard mesh) pricing page - live capture 2026-09-29Tailscale (managed WireGuard mesh) apps / download page - live capture 2026-09-29
Before you pay: check the renewal price, the refund window, and whether a cheaper or free path covers your use case - the honest checklist.
Based on our checks as of 2026-11-02: Tailscale (managed WireGuard mesh) scores 4.9/10 in our weighted review. We logged 3 red flags (listed above). User reports, ownership and the incident record are documented with dated sources in the meta-review below.
What do I actually get with Tailscale?
You get a managed WireGuard mesh that connects your devices securely with end-to-end encryption. The free plan allows 6 users and unlimited devices; business tiers add policy controls and support. Traffic flows peer-to-peer or via DERP relays, and exit nodes let your devices route through your own servers.
What is the renewal price and total cost over three years?
The monthly rate is $8 per user, with no change at renewal - the renewal ratio is 1. Since pricing is flat and recurring, the three-year cash total is not precomputed, but you’ll pay $8 per user each month indefinitely.
What proof is there for Tailscale’s no-logs claim?
There is no independent public audit of the closed-source coordination server. The logging claim is "policy-only" - Tailscale says it collects only metadata (device info, connection logs), but this can’t be independently verified. DERP relay code is open source and doesn’t log, and SOC 2 reports are available only on request.
Can I use Tailscale in a censored country like China or Iran?
No. Tailscale lacks obfuscation and uses standard WireGuard traffic patterns that are easily detected and blocked. It is not suitable for bypassing state-level censorship. Use tools designed for obfuscation, like Shadowsocks or customized WireGuard with cloaking.
Can I pay anonymously or sign up without an identity?
No. You must sign up using an email or SSO identity (Google, GitHub, etc.). True anonymity isn’t possible on the hosted service. For anonymous-adjacent use, self-host Headscale with a private auth backend or run plain WireGuard without a coordinator.
What happens if Tailscale shuts down or gets acquired?
If Tailscale shuts down, hosted users lose coordination. Self-hosted Headscale users remain unaffected. The client is open source (BSD-3), but the control plane is not. Acquisitions (like Border0) suggest enterprise focus, but the free tier has been preserved and expanded so far.
What’s the honest free or cheap alternative?
Use Headscale - a fully open-source, self-hosted Tailscale-compatible control plane - or plain WireGuard for full control. For consumer privacy, consider Mullvad (audited no-logs, flat pricing) or IVPN (independent, transparent). These cost money but don’t rely on trusting a closed coordinator.
The meta-review: what the internet says about Tailscale (managed WireGuard mesh)
We do not expect you to trust us. This review is a meta-review: below you see what other review sites claim - with their conflicts of interest labeled - what users report on Reddit and forums, and who actually operates Tailscale (managed WireGuard mesh). Every claim links to its source so you can verify it yourself.
What other reviewers say (1)
Every source carries a conflict label from our review-site database. "Affiliate-funded" means the site earns money if you buy what it recommends. We include critical voices deliberately.
Fetched 2026-11-02: small independent editorial review (monetization unknown). Honest scoping: Tailscale is 'not a VPN in the sense most VPN reviews use the word'. Likes the generous free plan and E2E encryption; dislikes the closed-source coordination server that sees device-to-device metadata, client logs streaming to Tailscale by default, non-refundable payments, and no public audit report (SOC 2 on request). Verdict: easiest way to connect your own devices; wrong tool for hiding your IP or streaming.
What users say (6)
Reddit, forums, HN - paraphrased and linked, never quoted out of context. Anecdotes, not proof - but refund complaints and leak reports are the best early-warning system this market has.
Fetched 2026-11-02 (25 comments): homelab texture - Plex/Jellyfin served over tailnets, subnet routers, Serve vs Funnel security advice, ephemeral-node Docker troubleshooting, awareness of the Tailscale SSH vulnerabilities via the official r/Tailscale post, distrust of third-party UIs.
Fetched 2026-11-02 (15 comments): Tailscale as the default way to close public exposure after Plex/Nextcloud zero-days; binding containers to tailnet IPs; 'Headscale can be used if you want 100% self-hosted'; one user moving public-facing services to SSO + Cloudflare instead.
Fetched 2026-11-02 (15 comments): r/VPN regulars recommend Tailscale exit nodes as the free way to get a home IP while traveling; one sarcastic 'beautiful disclosure' jab after the SSH patch; exit node on Apple TV or Pi suggested.
Thread page fetched 2026-11-02 (HTTP 200), comments via HN Algolia API: accurate framing that the flaws require an already-authorized tailnet peer, Headscale users affected too (bug in tailscaled), 'nearly everyone uses zero advanced features', plug for Headscale/NetBird, praise for the fast fix.
Fetched 2026-11-02 via GitHub API: the original community request to open-source the coordination server ('it would be even more perfect if the server was open-source'), opened June 2020, closed December 2022 without the server being open-sourced; the issue that seeded years of Headscale advocacy.
Fetched 2026-11-02 (9,881 comment hits for tailscale; 2,276 for headscale): HN treats Tailscale as core homelab/devops infrastructure - recommended by default, incident discussed with technical precision, Headscale normalized as the self-host answer.
AI fact summary - everything we know, compressed
Generated by Qwen3 on 2026-11-02 from our fact database plus the linked sources. It summarizes - it does not add facts. Check anything that matters against the linked sources.
Bottom line: Tailscale is the easiest way to connect your own devices securely via WireGuard, with a generous free tier (6 users, unlimited devices). It is not a consumer VPN and does not hide your IP from websites or provide anonymity. Traffic is end-to-end encrypted, but the coordination server sees metadata about which devices talk to which, including public IPs and connection patterns.
The logging truth: Tailscale claims it cannot read your traffic due to WireGuard encryption, which is accurate - payloads are safe. However, it admits to collecting device metadata, connection logs, and traffic statistics (Inter-Node Traffic Logs), stored in Canada, the US, Germany, and the UK. This metadata collection is confirmed in its privacy policy and security page; the closed-source control plane cannot be independently verified, and audits (SOC 2, Latacora) are not public.
Pricing reality: The Personal plan is $0 forever with solid limits (6 users, unlimited devices). Business tiers start at $8/user/month with no intro discount, and payments are non-refundable per the Terms. No billing traps beyond the hard renewal terms - pricing is flat and transparent, but you lose money if you cancel.
What reviewers say vs what users say: Independent reviewers like The Proof Desk stress Tailscale’s misclassification as a VPN, praising its encryption and free tier but criticizing the closed control plane and default client logging. Users on Reddit and HN overwhelmingly praise it for homelab and self-hosting use, though the October 2026 Tailworm incident sparked debate - some dismissed the risk (required prior access), while others questioned trust in the platform, showing a split between operational utility and security paranoia.
Who runs it: Tailscale Inc., based in Toronto, Canada, founded in 2019, operates the service. It has raised $275M and is pivoting toward enterprise identity and AI governance, acquiring Border0 in 2026. The company tolerates self-hosted alternatives like Headscale but keeps its control plane closed, making full trust unavoidable for hosted users.
Sources & how this review was built
Every external source used on this page, with the date we fetched it and its evidence class [A]-[D] (A = primary/operator, B = serious press/research, C = community, D = our own measurements). Methodology: how we verify. Sources disappear or change - if a link is dead, tell us via contact.
Evidence classes on this page:[A] A: 11[B] B: 8[C] C: 6[D] D: 0(D stays empty until our own test phase)
The most credible self-hosting on-ramp in the VPN space, built by and for people inside the censorship: the app is free and open source, you connect it to your…
auditedopen source
intro $5 /mo
Cyprus (EUPHORIATECH LIMITED, Nicosia, reg HE 484287 per site footer, verified 2026-11-02; IP rights in Portugal with Amnezia LDA, ops in Estonia) - for self-hosted users the operative jurisdiction is wherever their own VPS is hostedself-hosted vpn 11 d ago
The incumbent of self-hosted business VPNs, and still a safe pick in 2026 - with one honest fork in the road. Access Server is the polished, supported way to…
auditopen source
intro $7 /mo
United States - OpenVPN Inc., Pleasanton, California (about page fetched 2026-11-03); a Five Eyes member countryself-hosted vpn 9 d ago
The most polished way to hand censorship-resistant access to people who cannot configure a VPN: a few clicks in the Outline Manager builds a Shadowsocks server…
auditopen source
intro $3 /mo
United States - Outline Foundation, 30 N Gould St. #57975, Sheridan, Wyoming (contact address in Terms of Service and on the Google Play developer listing); ToS governed by Wyoming law. The software itself has no jurisdiction: the operative jurisdiction for a self-hosted user is wherever their rented VPS is located and the laws governing their cloud provider.self-hosted vpn 10 d ago



No comments yet - be the first. Posting runs a short proof-of-work in your browser (anti-spam), no account needed.